
Object Storage
Secure, S3-compatible object storage for cloud-native applications, backups and archives, dedicated to your organisation.
S3-compatible, highly secure object storage in the cloud
Store and access unstructured data
Keep your unstructured data in buckets. Creating buckets and uploading, listing and reading objects use standard S3 operations.
Build powerful cloud-native applications
Your applications reach the S3 API with path-style or virtual-hosted-style addressing.
Store your backups and archives
Write continuous database archives and Kubernetes backups to an S3 target. The same technology holds the off-cluster archive of the platform's own databases.
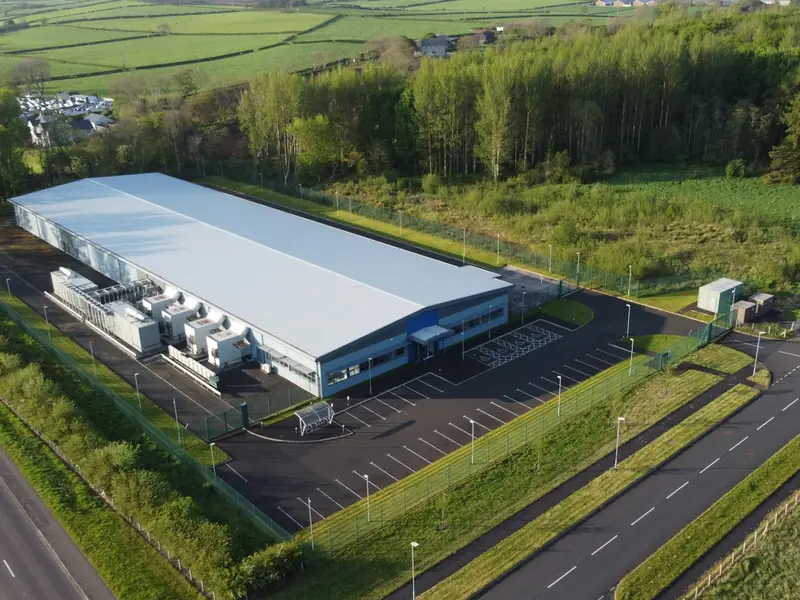
Keep your data in Türkiye
Your objects are stored in data centres in Türkiye.
Example scenarios
An app storing user files in S3
The app writes and reads files in buckets with standard S3 calls. Existing SDKs keep working with only the endpoint address changed.
A team keeping its database archive outside the cluster
Continuous database archives and Kubernetes backups are written to an S3 target. Storage is dedicated to the organisation, with its own endpoint and its own certificate.
A company bringing its data back from another cloud
The transfer is verified object by object. A line-by-line guide is prepared for the developer to adapt the signature differences in the app.
Key features
Storage dedicated to your organisation
Each organisation gets its own storage instance, with its own endpoint, TLS certificate and set of users and permissions. No shared pool.
Work with your existing S3 tools
S3 command-line tools, SDKs and your existing backup tools work by changing only the endpoint address, so you don't rewrite your code.
Manage your own keys
You generate access keys yourself in the object storage view of the cloud portal. Your buckets are managed from the same portal.
Move from another cloud with confidence
Migrations from a hyperscale cloud provider are verified object by object. Your developers get a line-by-line guide for any signature differences in the application.
Embedded security
Signed requests
Every request is signed and authenticated with S3 signature version 4 (SigV4).
Encryption in transit
Connections to the endpoint are encrypted with TLS, and certificates renew automatically before they expire.
Internal traffic encrypted too
Traffic between the storage service and your organisation's storage instance also uses TLS.
Learn more to get started
Kubernetes
See how to run containerised applications and their backups in the cloud.
Software Companies
Solutions for teams that build and run their applications in the cloud.
Cloud Migration
See the steps for moving data and workloads from another environment.
Infrastructure
Learn about the data centres where your data is stored.